
On this page3 sections
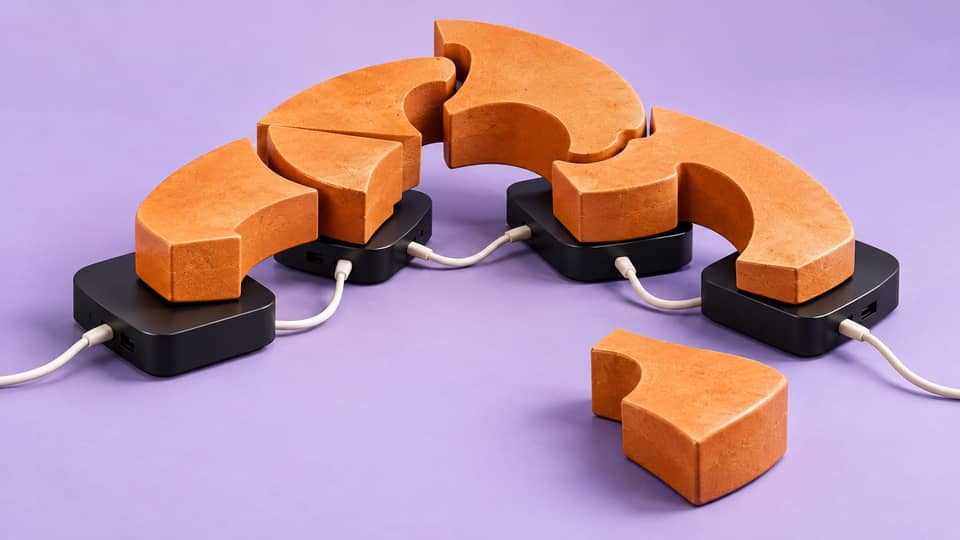
Fifteen inexpensive TV boxes, wired together, running one AI model: that is one striking image in Anthropic's October 12 self-replication report. An agent setting up a model on other machines is another. Put those pictures together carelessly and you get a third story, a small AI worm spreading through consumer devices, that the study did not demonstrate.
The work asks serious questions about models running beyond a provider's datacenter. To understand its answers, keep the two experiments separate. That distinction also helps an operator looking after cameras, gateways or other small computers ask a practical question: if a model were running here, what would actually stop it?
The TV boxes and the replication test
In the physical demonstration, Gemma4-26B-A4B ran across 15 Android TV boxes. The replication test used a different setup: a firewalled cloud fleet running Android emulation, with a deliberately simple, unauthenticated way in. GLM-5.2 completed that simplified task while its own model was served separately. The target machines set up Llama3.1-8B.

That last distinction is easy to lose. The acting model could arrange for another model to run on the target machines; it was not hosting itself on each consumer device it reached. The researchers distinguish the capability needed to complete replication from the model size their devices could hold. In their tested models, those requirements did not yet meet. Their estimate for the end of 2026 extends a general capability trend; it is not a measured deadline. The primary report gives the conditions beside the results.
Think of what happens when we mentally borrow the hardware from the first experiment and the successful agent from the second. We have assembled a system the researchers did not run. A benchmark result belongs to the model, the software guiding its work, the configuration and the conditions that produced it. Those details are part of the result, even when the headline has no room for them.
The deliberately easy access path still makes the experiment worth reading. It gives a defender a concrete condition to look for: could equipment in this fleet be reached and made to execute software in a comparable way? That is a more useful investigation than either treating a laboratory success as an outbreak or waving it away because the laboratory was simplified.
A stop button has to stop the right thing
Consider a hypothetical camera gateway already holding a model and the software needed to run it. The team blocks its access to a hosted AI service. The network rule can work perfectly while the gateway keeps computing locally. The rule removed one route to an answer; it did not remove the model on the device.
Blocking a provider account, denying a network connection, ending a process and separating devices act in different places. The useful choice follows what must be interrupted. Can the program still run? Can it still reach another machine? Observing those actions tells you more than the successful completion message from the change that was meant to prevent them.
The existing protections also matter. If a fleet cannot execute unapproved software and the relevant network separation has been verified, this study is not evidence that those controls were bypassed. If software state or device access is uncertain, the absence of a reported AI outbreak does not settle it. The team still needs to identify the equipment and configuration in question, then decide what to test, contain, retire or knowingly leave exposed.
The report helps draw the questions. The fleet supplies the answers. Keeping that division clear makes the research useful without asking it to prove what happened on machines the researchers never examined.
Optional worked example: checking a camera fleet's stop button
In our hypothetical organization, a team blocks hosted model APIs and reports that its camera gateways can no longer run an AI agent. To examine the claim, first put two sentences side by side: “the gateway cannot contact the hosted model API” and “the gateway cannot continue running a local model.” One concerns a connection; the other concerns a program. They need different observations.
Suppose the next question is whether the gateway can reach another device. An authorized, isolated test can use harmless traffic and a receiving endpoint the team controls. Begin with a permitted control path and check that the receiver records the expected probe. Otherwise, a silent receiver might simply be a receiver that is not watching.
Once that observation works, test the prohibited path and compare the receiver's record with the relevant enforcement record. An application's error message alone cannot show where the request stopped. Even a well-observed denial supports a conclusion about this path and configuration, not every route into the destination.
| Claim for the hypothetical fleet | Evidence that would support it | What remains outside that claim |
|---|---|---|
| The tested hosted-API path is denied. | The intended deny rule, enforcement record, and verified receiver observation for that test. | Local inference and other destinations or access paths. |
| The reviewed local model process has stopped. | Process and service state checked on the affected device. | Another executable or a later restart. |
| The tested gateway path into the protected segment is denied. | The relevant policy and enforcement record, with a known receiver whose observation works. | Untested routes, configurations, or device populations. |
The rows separate three things a team might otherwise call “blocked.” A stopped local process can restart later. A denied network path leaves other destinations untested. An unobserved receiver leaves the outcome unknown. These are proposed defensive checks, not tests performed for this article or validated detectors for an AI worm.
For gateways still untested, the team must choose what to test, contain, retire or knowingly leave exposed; the risk-treatment walkthrough follows that decision. Back at our camera, a denied hosted-API request could coexist with a local model still running. Checking the device’s process and service state answers a different question from watching the receiving endpoint. Until those observations are available, the quiet network is not a stopped program.
Sources and scope
The experimental summary follows Anthropic's October 12, 2026 study, discovered through the LocalLLaMA discussion. The fleet example and defensive checks are original hypothetical teaching examples. No device exploitation, model execution, containment trial, author incident, or real-world replication result is claimed.
Source context
Source links appear within this article. Read them alongside the author’s analysis and evaluate the guidance against your environment.
Report an error or outdated detail